
PCI DSS v4.0.1 · ISO/IEC 27001:2022 · NIST CSF 2.0 · SOC 2 (Trust Services Criteria) · GDPR (EU 2016/679)
Assess once. Compliant everywhere. One control, 9 frameworks, zero drift.
Stop updating the same control in five different trackers. Set a verdict once and every framework that shares that control stays aligned automatically.
Built for banks, fintechs, payment processors and the regulated industries that answer to more than one framework at a time.
Kim's Unified Cybersecurity Framework Tool
✓ Updated for SCF 2026.3 — 22 Sep 2026
No charge for 7 days. Cancel before the trial ends and nothing is taken. Already have an account? Sign in.
What changes
One workspace instead of five trackers
Before
- A separate spreadsheet for each framework
- The same control answered differently in three places
- Evidence scattered across mailboxes and shared drives
- Cross-mapping done by hand, and out of date the day after
- No single answer to “where are we?” before a board meeting
- Audit season spent rebuilding the pack from scratch
After
- One workspace covering every framework you hold
- One verdict per control, carried to its equivalents automatically
- Evidence attached once, following the crosswalk to every linked control
- The mapping shipped with the product and maintained for you
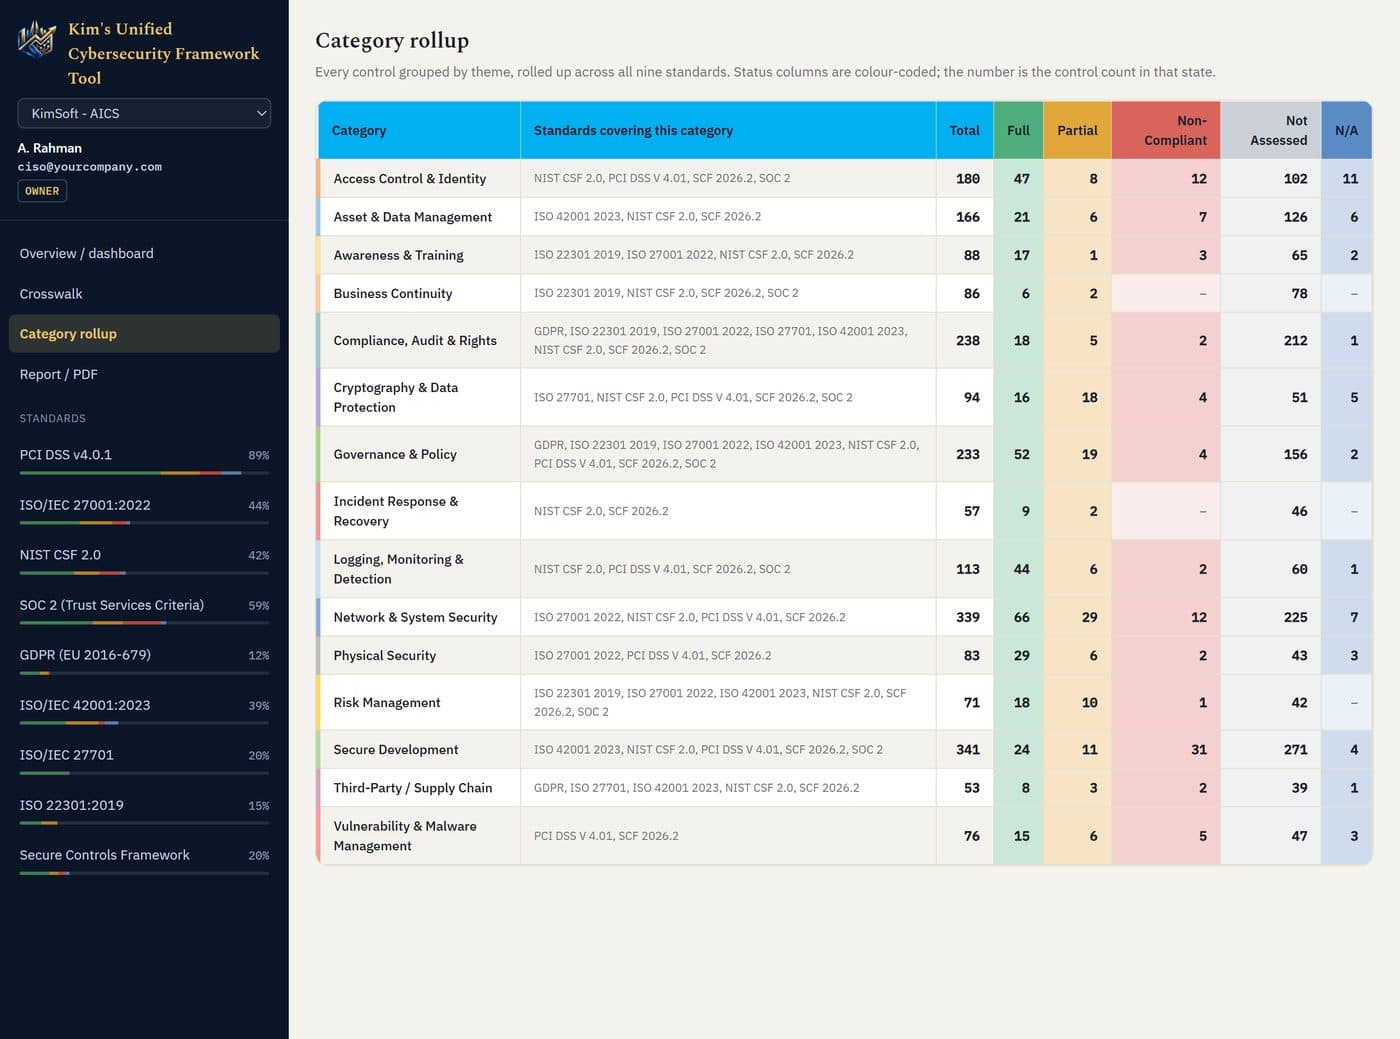
- A live dashboard, by framework and by category, at any moment
- A board-ready PDF and an evidence pack in two clicks
See it
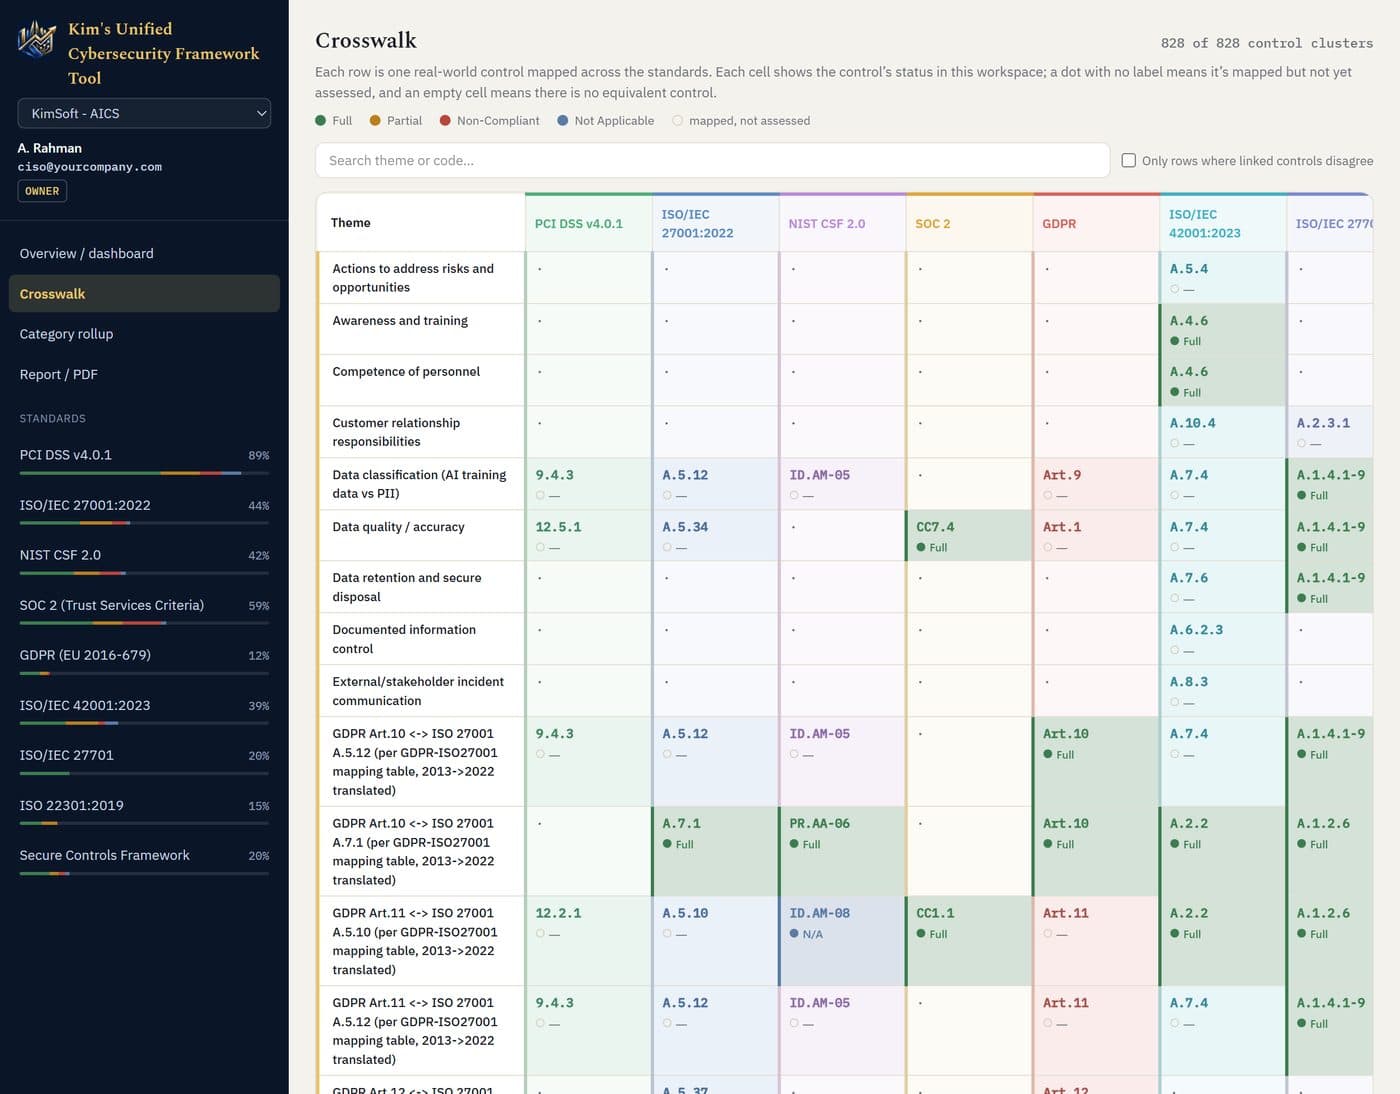
The product, not a mock-up
Screens from a live workspace mid-assessment.


Who it is for
Built for the teams that carry the obligation
Banks and financial institutions
PCI DSS, ISO 27001, SOC 2 and NIST CSF from one control library, with the same answer for the regulator, the auditor and the board.
Fintechs and payment processors
PCI DSS v4.0.1 and ISO 27001 in one place, with the overlap between them mapped rather than re-answered.
Telecoms and government entities
ISO 27001, NIST CSF and ISO 22301 side by side, so continuity and security evidence is collected once.
Privacy teams
GDPR and ISO 27701 alongside the security frameworks, so a privacy control and its security equivalent are answered once.
Consultancies and advisers
A separate workspace per client, each billed and isolated on its own, and reports that carry your client's branding rather than ours.
Audit firms
Read-only seats for reviewers, an evidence pack as a ZIP with a manifest, and a PDF that states scope and period per framework.
Why it is different
Not another control spreadsheet with a login
- 2,275 controls pre-loaded across 9 frameworks, with the Secure Controls Framework as a spine — nothing to configure before you start.
- 828 cross‑standard mappings maintained for you, rather than a mapping exercise you run yourself every time a standard moves.
- A real crosswalk, not a theoretical mapping — clusters taken from published cross-reference tables, so one verdict carries to the equivalent clause in the other standards.
- Evidence follows the map. Attach a file once and it appears on every linked control.
- Baseline push: work your strongest framework end to end, then apply it across the crosswalk in a single action. Manual overrides are preserved.
- Multi-tenant SaaS with database-enforced isolation, mandatory two-factor authentication, and no card data on our servers.
- White-label reporting: your logo, your header and footer, on every page.
- Built by a practitioner who ran these programmes, not a generic SaaS company that added a compliance module.
Who built it
Founder-led, practitioner-built
“I built this after years of running the same controls through a different spreadsheet for every framework, rulebook and standard. It is designed, maintained and supported by me, from the Kingdom of Bahrain.”
— Kim · kim_abdalian@yahoo.com
Pricing
Priced per seat, with nothing held back
$1,000
per seat / year
Limited launch offer — $5,000 per 5-seat pack. Price rises after the first cohort.
- 5-seat minimum — $5,000 for the first year
- Add or remove seats one at a time, pro-rated
- Seats reassignable for the whole term
- 7-day free trial, cancel any time
- Every feature included — no tiers, no add-ons
What it replaces
- The five-to-seven spreadsheets one programme usually runs on
- The hand-built cross-mapping between them, and the drift that follows
- The scramble to assemble an evidence pack at audit time
- The 828 shared requirements you would otherwise map by hand
Security & architecture
Built to be looked at by the people you answer to
Tenant isolation in the database
Every row carries an org id and PostgreSQL Row-Level Security enforces it. A query that forgets the filter returns nothing, not someone else's data.
Evidence in a private bucket
Never public. Files are served through signed URLs that expire in 60 seconds.
Encrypted in transit and at rest
TLS 1.2 or better on the wire, AES-256 at rest.
Two-factor authentication, mandatory
Every account, no exception, with a 30-minute idle timeout and 90-day password rotation.
Backed up daily, with point-in-time recovery
So a bad afternoon is recoverable, not a rebuild.
Hosted in the EU
Frankfurt (eu-central-1). Evidence and assessment data stay in the region.
Sessions end on their own
A 30-minute idle timeout, shared across open tabs, so an unattended screen does not stay signed in.
No card data on our servers
Payments are taken by Lemon Squeezy as Merchant of Record, which also handles global VAT and sales tax.
Questions
Asked before you have to ask them
How is evidence stored?
In a private bucket, never public. A file is served through a signed URL that expires in 60 seconds, so a copied link is useless a minute later. Attach a file to one control and it appears on every crosswalk-linked control in the other standards, tagged with where it came from; remove it once and it is gone everywhere.
Can we export everything?
Yes, and without asking us. A board-ready PDF, a CSV of any selection of standards, and an evidence pack as a ZIP with every attached file foldered by standard and control plus a manifest. There is no lock-in: your assessment data leaves in open formats whenever you want it.
How does tenant isolation work?
Every row carries an org id and PostgreSQL Row-Level Security enforces it in the database, not in application code. A query that forgets the filter returns nothing rather than someone else's data. Server Actions re-check role and membership on every write.
What happens when a standard is revised?
The control library is reference data maintained centrally and shipped to every workspace. Your statuses, notes and evidence are yours and are never touched by an update.
What if someone leaves?
Seats are reassignable for the whole term. Remove a member and the seat frees immediately for the next person, at no extra cost.
Start with your strongest framework. The rest follows.
7 days free with every feature on. Work one standard end to end, push it across the crosswalk, and see the others move.
Prefer to talk first? kim_abdalian@yahoo.com · WhatsApp +973‑3671‑9993
Made in Bahrain · Serving the GCC and beyond · Founder-led, practitioner-built
Covering: PCI DSS v4.0.1 · ISO/IEC 27001:2022 · NIST CSF 2.0 · SOC 2 (Trust Services Criteria) · GDPR (EU 2016/679) · ISO/IEC 42001:2023 · ISO/IEC 27701 · ISO 22301:2019 · Secure Controls Framework.
© 2026 Kim. All rights reserved.
“Kim's Unified Cybersecurity Framework Tool” and its structure, control taxonomy, category framework, and cross‑standard crosswalk mappings are the proprietary intellectual property of Kim. Unauthorized copying, reproduction, distribution, sublicensing, or resale — in whole or in part — is strictly prohibited without prior written consent. Access is licensed, not sold, subject to the accompanying End User Licence Agreement.
Contact Kim · kim_abdalian@yahoo.com · +973‑3671‑9993
Pricing · Terms of Service · Privacy Policy · Refund Policy · Security Policy